
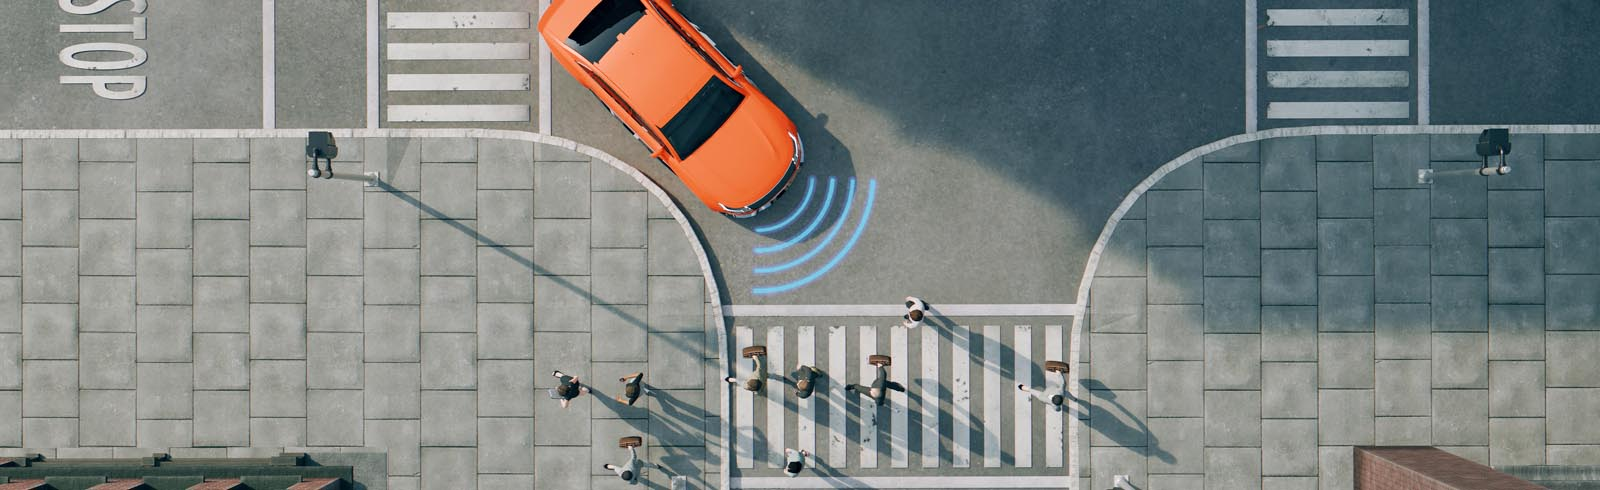
Machine learning has rapidly become a driving force behind artificial intelligence innovations, powering autonomous vehicles, smart medical devices, and advanced industrial robots that work closely with humans. As these systems transition from theory to real-world deployment, they promise transformative efficiency and convenience. Yet, they also introduce critical safety concerns that cannot be ignored.
George Pappas, Associate Dean of Research at the University of Pennsylvania’s School of Engineering and Applied Science, emphasizes that while machine learning has enabled impressive capabilities, it currently falls short of the precision expected in life-or-death environments. He highlights a staggering contrast: while many machine learning models are celebrated for achieving accuracy rates of 95 to 97 percent, safety-critical systems such as autonomous cars or medical robots require nearly perfect reliability, on the order of one error in a billion—equivalent to a 99.9999999 percent success rate.
Pappas chaired a National Academies study committee that recently released a comprehensive report addressing this exact issue. The findings were discussed in a public webinar, where he and fellow committee members outlined how to close the performance gap between current machine learning capabilities and the stringent demands of safety-critical environments.
Why Machine Learning Falls Short in Safety-Critical Systems
Machine learning systems function by analyzing large amounts of training data and using statistical patterns to make decisions or predictions. This approach works well when data accurately reflects real-world conditions. However, when the data is incomplete, unrepresentative, or collected without consideration of deployment conditions, major risks can arise.
Thomas Dietterich, Distinguished Professor Emeritus at Oregon State University, notes that training data is often gathered as a byproduct of normal business operations rather than being tailored for safety-critical applications. This disconnect means that machine learning models may not be prepared to handle the full range of environmental conditions in which they will operate. Weather changes, unusual lighting conditions, or unexpected objects can confuse systems that were not trained with comprehensive real-world scenarios.
Novelty poses another major challenge. Machine learning models are highly dependent on the patterns found in their training data, which means they may fail when they confront situations never previously encountered. For example, an autonomous car might not recognize a unique animal crossing the road, or a factory robot might misinterpret a new type of tool as a movable object.
Dietterich explains that current systems often lack mechanisms for detecting when they have encountered unfamiliar situations. He argues for the implementation of external monitoring loops capable of identifying such novelties, categorizing them, and facilitating a rapid feedback process wherein additional data can be collected and the system retrained and validated.
Designing Systems with Built-In Uncertainty Awareness
One of the key insights from the report is that uncertainty is inherent in machine learning models, and safe system design must account for this fact. Instead of assuming high-confidence predictions at all times, machine learning components should be able to signal when their uncertainty is elevated. When operating under uncertain conditions, autonomous systems—such as self-driving cars—should adjust their behavior accordingly, slowing down, collecting additional environmental data, or switching to human oversight or safer fallback strategies.
Dietterich underscores the need for architectural transformations that introduce redundancy and guardrails. For instance, if a system fails to accurately detect an obstacle or miscalculates the distance to another vehicle, secondary systems must be prepared to intervene. This could mean using additional sensors, alternative algorithms, or rule-based safety measures as a backup to machine learning models.
Pappas echoes this need for protective frameworks, stating that safety filters and fail-safe guardrails must be systematically embedded into any system operating in high-risk environments. If a robot misidentifies a human as an object, safeguards should immediately activate to prevent harm.
Standards, Regulations, and Transparency as Public Trust Foundations
Beyond technical architecture, the report stresses the importance of establishing robust regulatory standards, safety testing methods, and accountability frameworks. As machine learning-driven systems become more integrated into society, public trust will depend on consistent safety performance and transparent reporting practices.
Jonathan How, Ford Professor of Engineering at the Massachusetts Institute of Technology, highlights the need for transparency in both technical evaluations and real-world performance reporting. This includes sharing safety incidents and near-miss events so that the broader engineering community can learn from failures and proactively improve system designs. Without openness and accountability, the development of trust in automated systems will be severely undermined.
Bridging Disciplines to Build a Safer AI Future
The report argues that creating safe machine learning-enabled systems requires the merger of two historically distinct fields: traditional safety-critical engineering and modern machine learning research. These communities differ in core values and design philosophies. Machine learning researchers often prioritize high average-case accuracy, while engineers working in safety-critical domains focus on worst-case reliability and risk mitigation.
Dietterich emphasizes this gap, noting that while machine learning celebrates generalization across varied environments, safety engineering often deliberately restricts operational domains to tightly controlled conditions to guarantee safety.
Pappas argues that integrating these perspectives will require a new interdisciplinary field focused on designing machine learning systems that meet the rigorous safety standards found in industries such as aviation, healthcare, energy, and transportation. This shift demands new engineering frameworks, shared terminologies, and collaborative research methodologies.
Building the Next Generation of Safe AI Engineers
According to How, developing safe machine learning-driven systems depends not only on technological advancement but also on workforce education. Training future engineers and researchers to understand both machine learning principles and safety-critical design is essential.
This educational focus should extend beyond academic institutions. Industry leaders must invest in upskilling their current engineering teams, ensuring that safety regulations, risk assessment methodologies, and trustworthy AI design principles are deeply embedded in development processes.
The Path Forward: Balancing Innovation with Responsibility
As AI-driven technologies increasingly interact with humans in real time, society faces a critical crossroads. Machine learning promises efficiency, automation, and innovation on an unprecedented scale. However, without rigorous safety measures, even minor failures can lead to catastrophic consequences.
The message from leading academic and engineering experts is clear: achieving safety in machine learning-based systems is not optional—it is essential. By improving data quality, preparing systems for uncertainty and novelty, introducing protective system architectures, establishing accountability standards, and fostering interdisciplinary collaboration, the industry can move toward a future in which artificial intelligence not only enhances human life but does so responsibly and safely.
Leave a Reply