
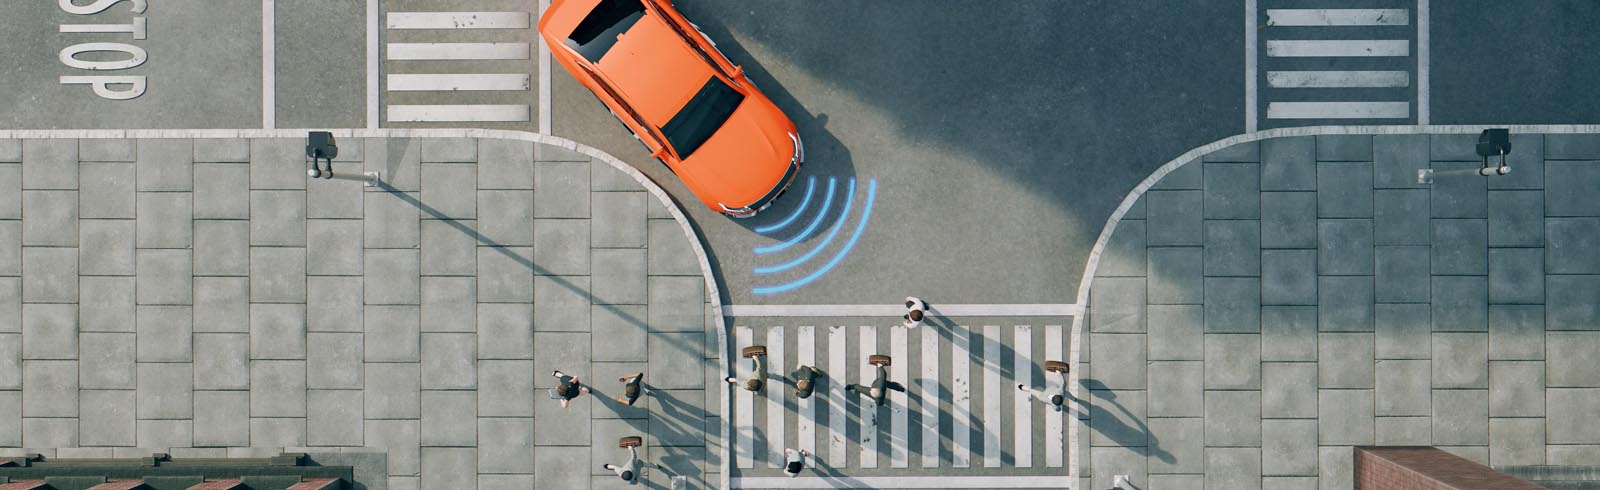
Machine learning has quickly become a foundational technology powering modern artificial intelligence applications, from autonomous vehicles navigating crowded city streets to medical devices assisting doctors in hospitals and advanced robots performing tasks alongside people. As these systems move closer to real-world environments and interact directly with humans, a critical question grows louder: how do we ensure they operate with the level of safety society demands?
Experts warn that while machine learning enables unprecedented autonomy and efficiency, it also introduces new and complex risks. A self-driving car might misinterpret a pedestrian’s movement. An industrial robot could confuse a worker for a piece of equipment. In high-stakes environments, even a single misjudgment can lead to serious harm.
George Pappas, associate dean of research at the University of Pennsylvania’s School of Engineering and Applied Science, notes that current machine learning performance metrics are ill-suited to safety-critical systems. In typical AI research, accuracy rates of 95 to 97 percent are often celebrated. But in systems like aviation, automobiles, or healthcare, reliability expectations approach near-zero failure — on the order of one error in a billion events.
“There is a critical gap between where machine learning stands today and what safety-critical systems require,” Pappas explains. He recently chaired a National Academies committee tasked with outlining a path to close this gap, focusing on improving both machine learning reliability and the broader systems in which AI components operate.
Designing Systems That Anticipate Uncertainty
Machine learning works by discovering patterns in data and applying those patterns to new situations. But as powerful as this approach is, it can be brittle. If the training data does not fully represent the real-world environments the system will face, the consequences can be dangerous.
Thomas Dietterich, distinguished professor emeritus at Oregon State University and a member of the committee, points out that many training datasets today are collected incidentally — gathered from internal company operations rather than intentionally designed for safety-critical learning. This can leave AI systems blind to rare but important scenarios.
Dietterich argues that training data must mirror real-world conditions as closely as possible. That means capturing the full diversity of environments, including lighting changes, weather variations, unusual objects, and unpredictable human behavior. It also means preparing systems for the unexpected. A self-driving car encountering a type of vehicle it has never seen before or a strange object crossing the road should not default to blind confidence.
“Machine learning systems tend to fail when they encounter novelty,” Dietterich says. To manage that risk, he advocates for systems capable of recognizing when they are uncertain. When uncertainty spikes — for example, when a car’s sensors are confused — the system should slow down, collect more information, and shift into a safer operating mode rather than pressing forward blindly.
These protective behaviors represent a new class of architecture for AI-enabled systems — one that not only learns but also monitors itself for potential failure. Built-in guardrails, redundancy, and backup strategies are essential, experts argue. If a primary AI component misinterprets a situation, a secondary logic-based safety system should intervene.
Every machine learning deployment in high-risk environments, Pappas emphasizes, must have “safety filters” capable of preventing harm if the AI makes a mistake. These safeguards give engineers the ability to stop accidents even when a system’s predictive model falters.
The Need for Standards, Transparency, and Oversight
Technical improvements alone are not enough. As AI systems become more embedded in daily life, there is a growing need for standards, regulation, and consistent testing approaches that benchmark safety. Jonathan How, Ford Professor of Engineering at MIT and another committee member, stresses that the current guidance around machine learning safety has not kept pace with industry adoption.
To maintain public trust, transparency is crucial. That includes detailed technical reporting and open disclosure of safety incidents — including near misses that could reveal hidden risks. Learning from real-world use is essential for improving AI reliability.
“As we deploy these systems, we must be honest about what goes wrong,” How says. Transparency helps not only engineers refine their systems but also public officials and communities understand how the technology affects them.
Bringing Together Two Engineering Cultures
Achieving safe machine learning at scale requires bridging two historically separate domains: the reliability-focused world of safety-critical engineering and the innovation-driven field of artificial intelligence research.
The machine learning community seeks broad generalization — the ability to perform well across a wide range of conditions. Safety-critical engineering, by contrast, often limits system behavior to tightly controlled environments to guarantee performance. These philosophies must merge to create a new engineering paradigm that combines adaptability with strict reliability.
“In safety-critical environments, we must prioritize worst-case performance, not average success rates,” Dietterich explains. A single rare failure in an airplane, operating room, or autonomous vehicle can be catastrophic, even if average performance is high.
Pappas believes this convergence will reshape engineering education. Students and working engineers alike must develop fluency in both machine learning methods and traditional safety assurance practices. Universities, he says, will need to train talent that thinks systematically about risk, verification, and trust — not just algorithmic innovation.
Industry, too, has a role to play. Companies adopting AI should invest in continuous training for their workforce to deepen their understanding of safety regulations and best practices for deploying machine learning responsibly.
A Future Built on Trust and Responsibility
Artificial intelligence is advancing rapidly, and its integration into society will only accelerate. With that progress comes opportunity — and responsibility. Ensuring safety in machine learning systems is not simply a technical challenge; it is a societal imperative. Proper safeguards, transparent standards, and cross-disciplinary collaboration are all essential as AI expands into areas where human lives and well-being are at stake.
The National Academies report serves as a reminder: while machine learning holds remarkable promise, achieving true safety requires commitment, vigilance, and innovation at every level — from algorithm design to system architecture to workforce education.
As AI systems take on bigger roles in transportation, healthcare, manufacturing, and beyond, the world will judge the technology not just by what it can do, but by how reliably — and safely — it performs.
Leave a Reply